
Defense-in-Depth for Hypervisors
ZeroLock® runs directly on the hypervisor to stop attacks before they start, catch what can get past, and undo the damage.
Unlike endpoint tools that operate inside workloads, ZeroLock protects the virtualization layer itself, where attackers can manipulate hosts, virtual machines, and storage simultaneously.
Hypervisor-Native Security Architecture
ZeroLock runs directly on the hypervisor to monitor and control activity at the virtualization layer, with no kernel modules and no changes to the hypervisor.
vCenter
ZeroLock
Applications
Guest Operating Systems
Virtual Machines
Endpoint Security
Network Security
Identity Security
Hypervisor
ZeroLock Hypervisor Security
Hardware
Infrastructure Security
Because protection occurs at the hypervisor layer:
- No agents are required inside virtual machines
- Guest operating systems remain untouched
- Controls apply to every workload on the host
- Visibility extends below the operating system
ZeroLock sees and controls activity at the layer where most security tools stop, which is exactly where attackers have moved.
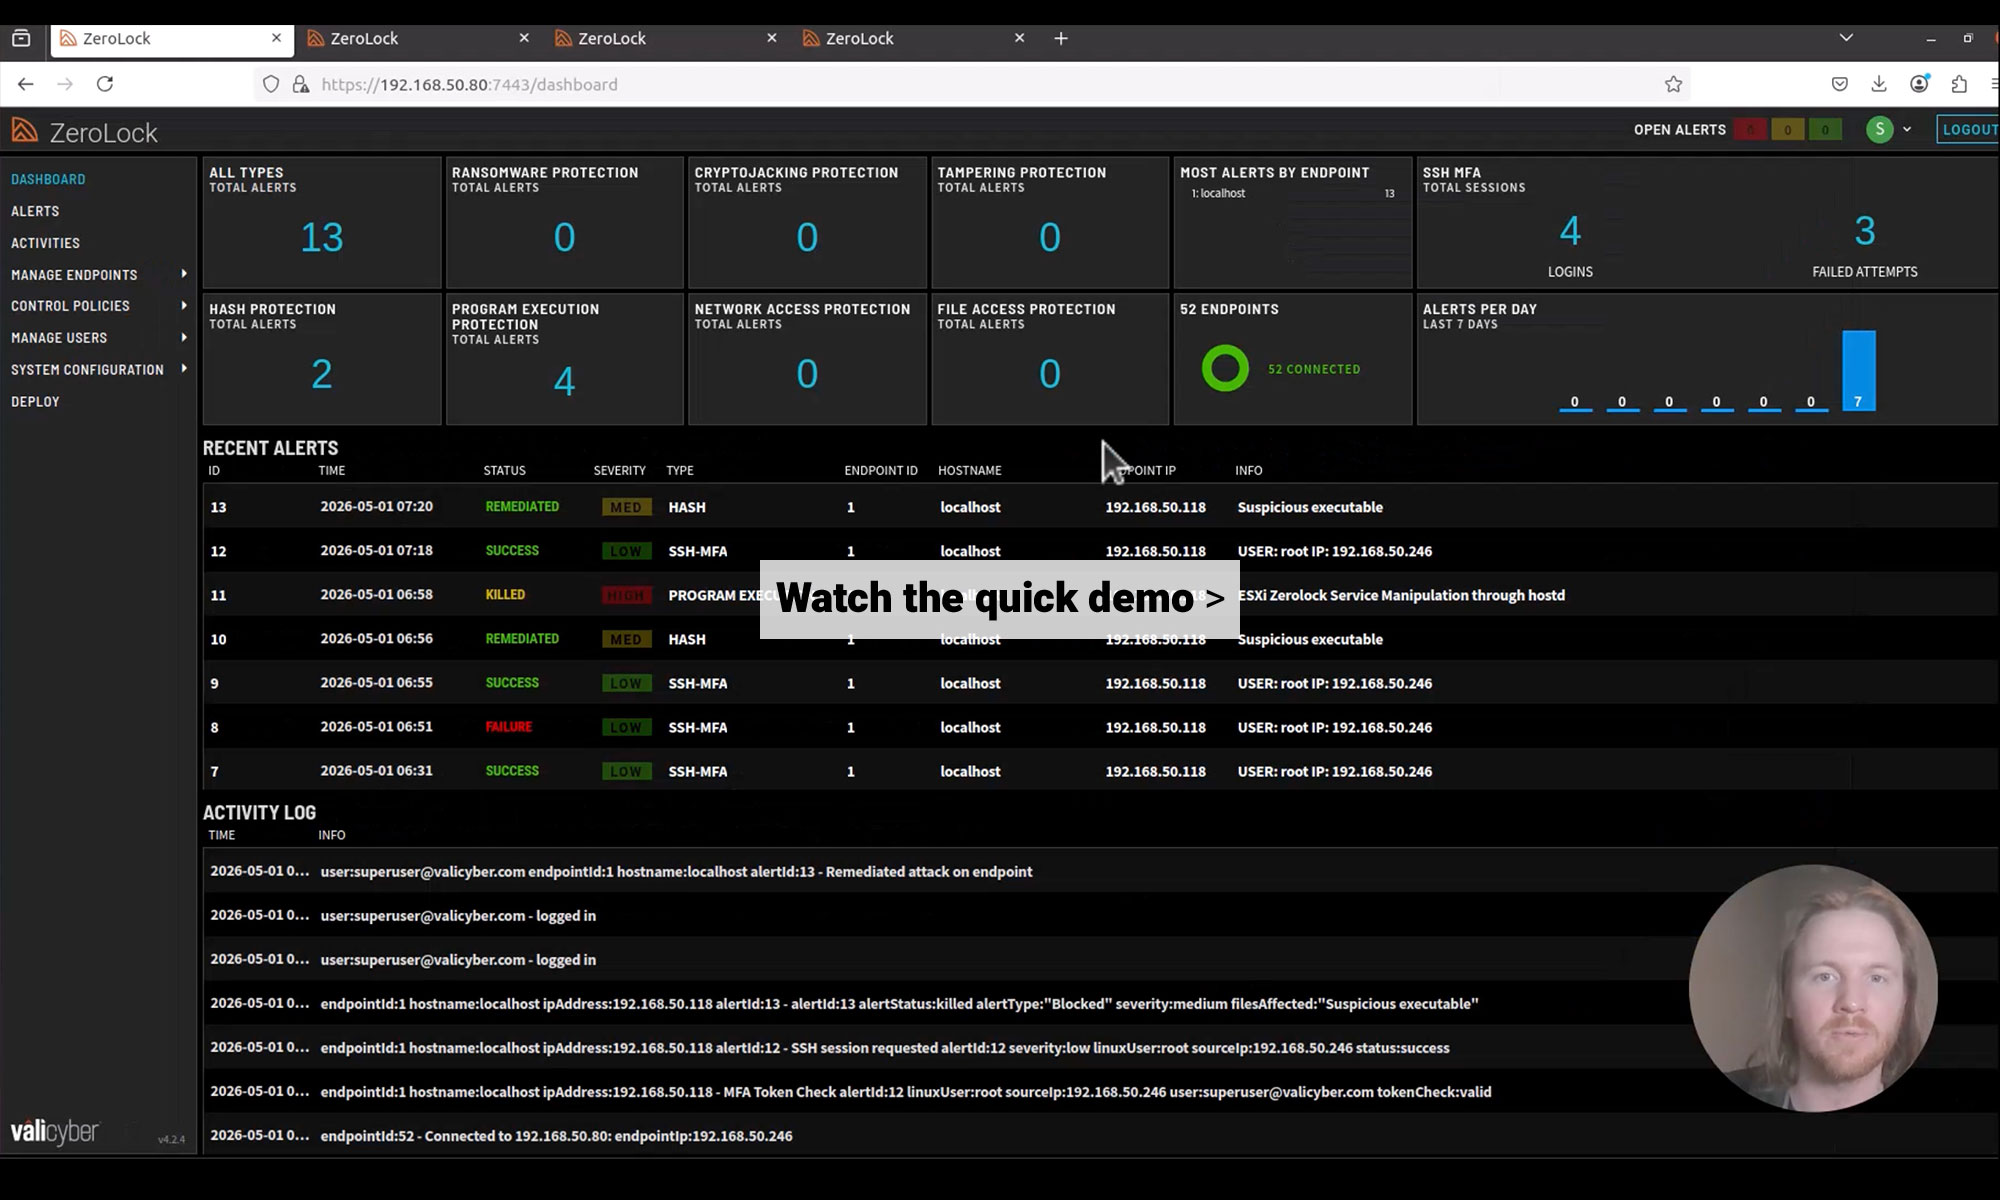
See Defense-in-Depth for Hypervisors in Action
Preempt
Stop attacks before they start.
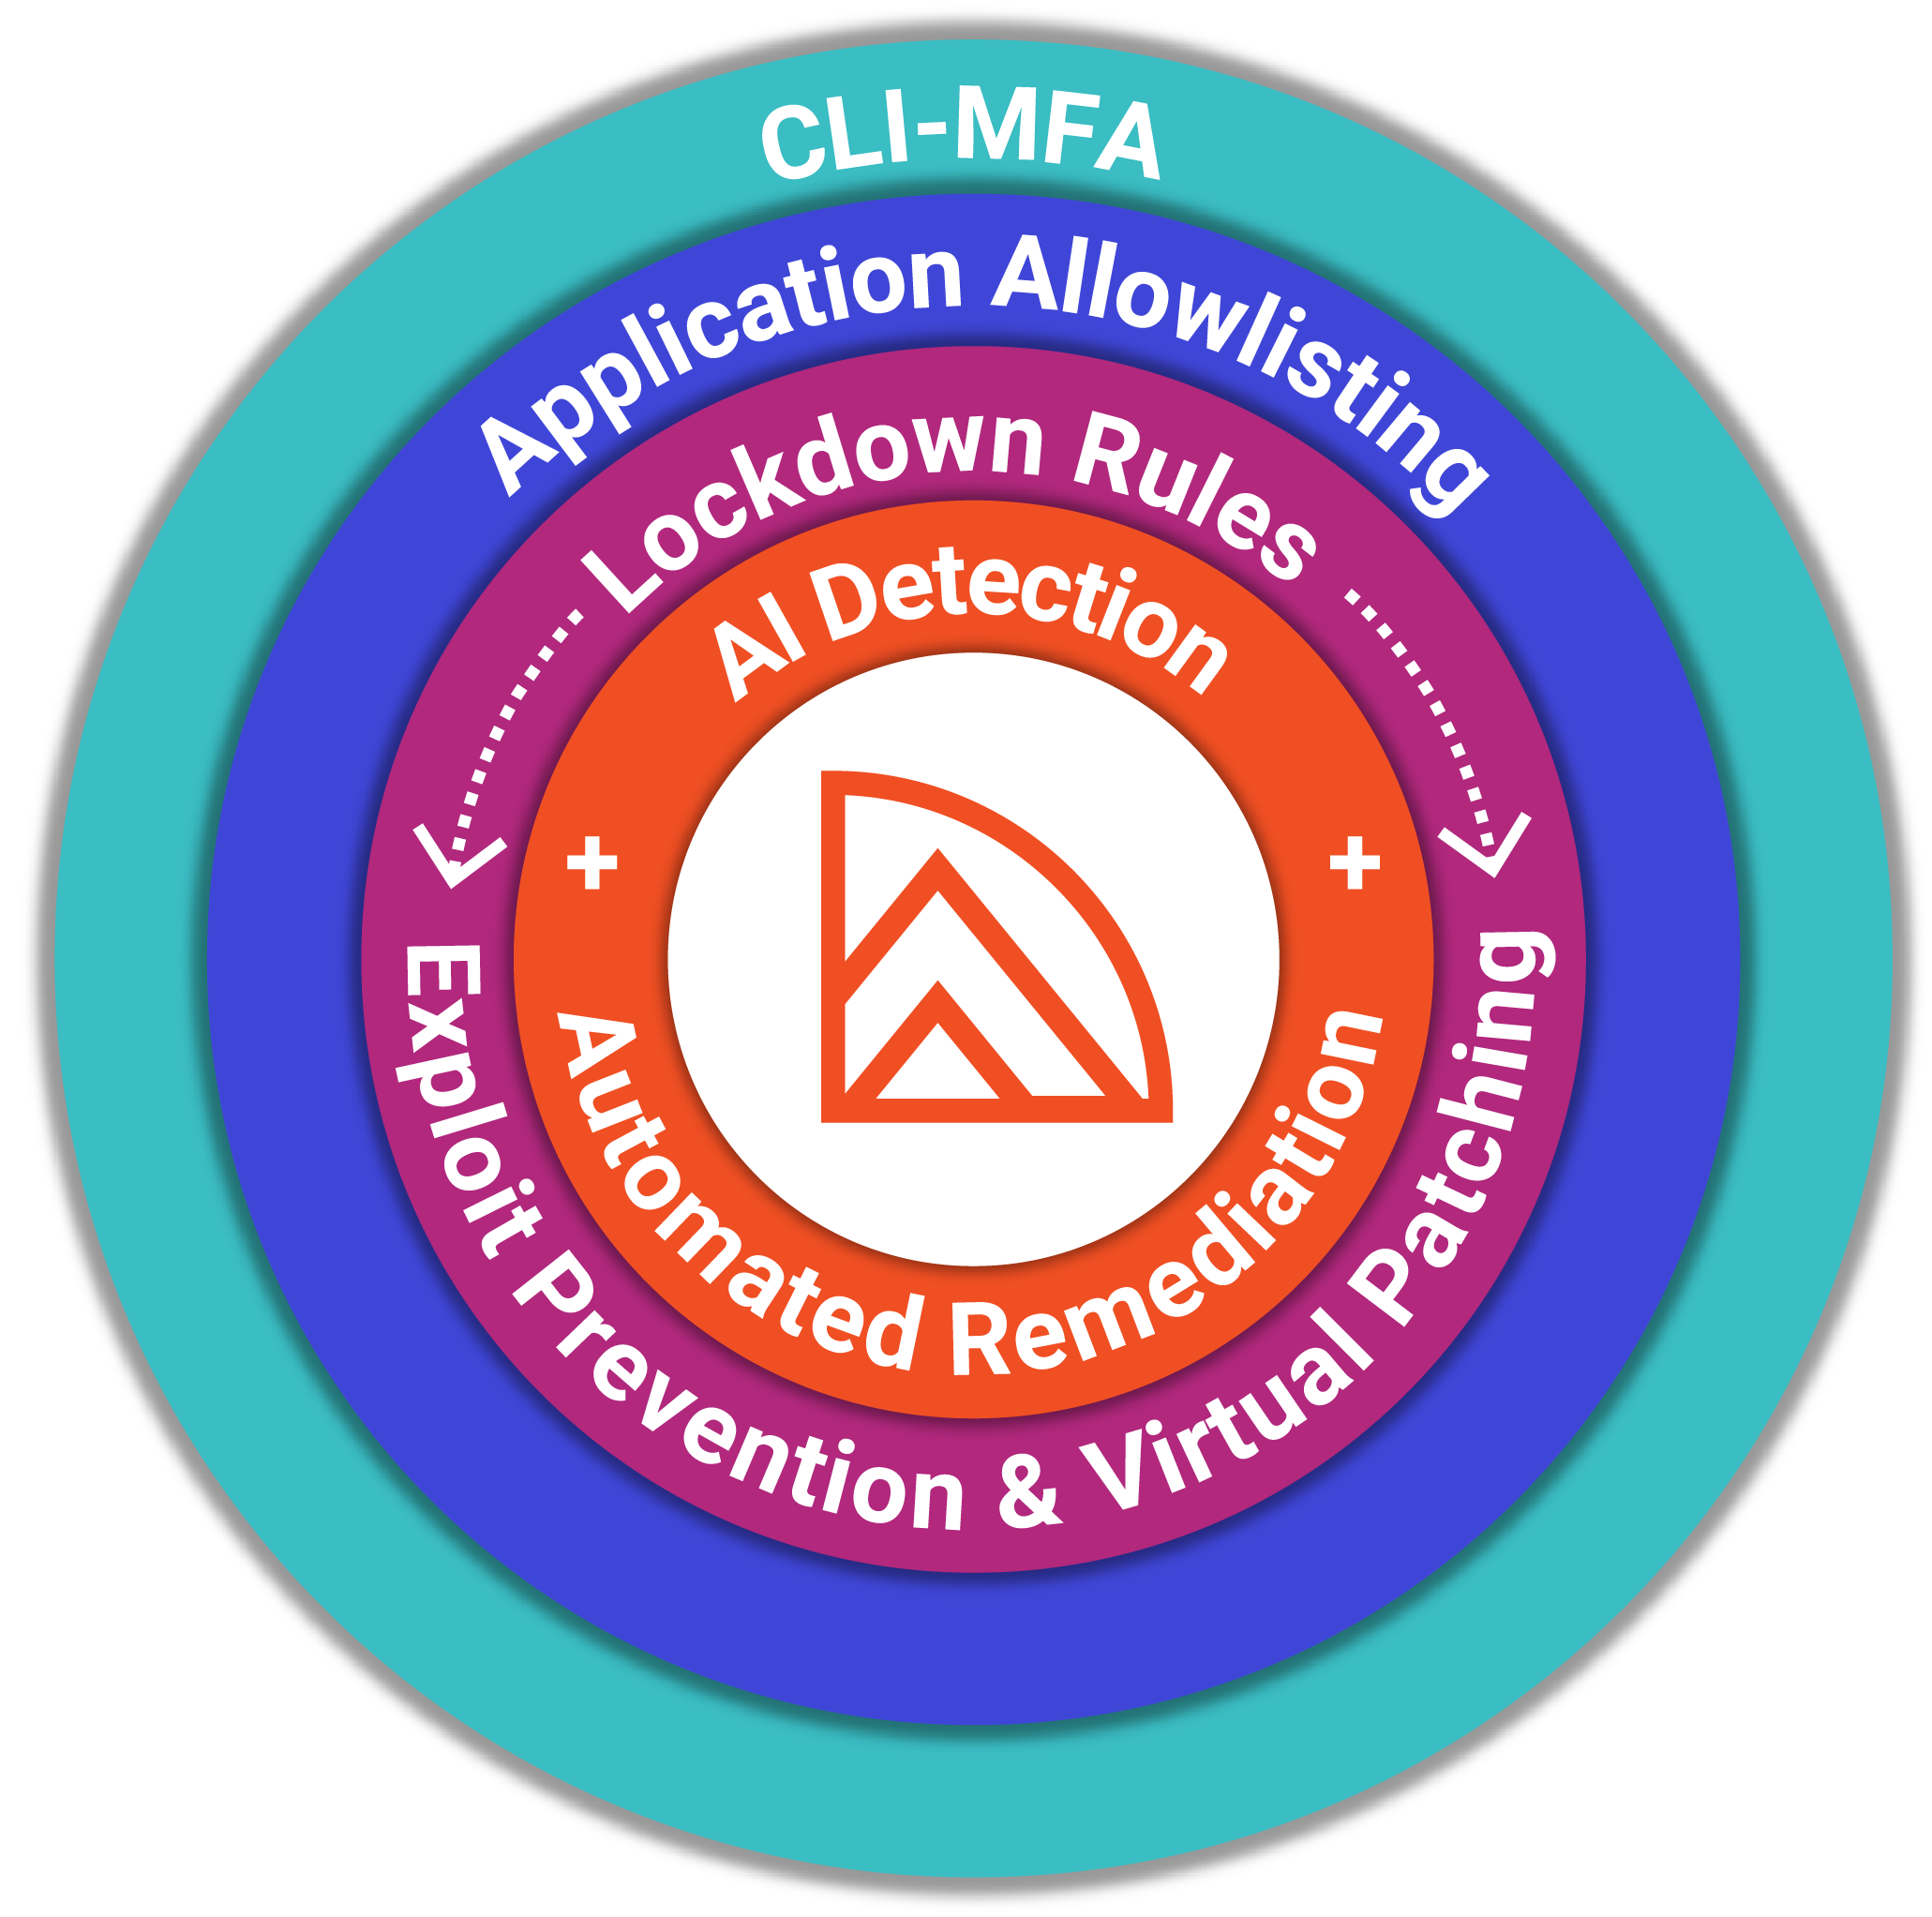
Attackers increasingly arrive with valid credentials or a fresh exploit. These controls stop them at the hypervisor, before they can touch workloads or infrastructure.
CLI-MFA
Exploit Prevention & Virtual Patching
Application Allowlisting
Data Exfiltration & File Access Prevention
Canary Files
Anti-tampering
Protect
Detect and undo what may get through.
No security strategy is static, which is why resilience matters as much as prevention. Patented AI behavioral detection runs inside the agent and catches what can get past, even attacks no rule anticipates.
AI Behavioral Detection
Ransomware & Wiperware Protection
Real-time Remediation & Automated Rollback
Process Tree Visibility
Perform
Built for how your team works.
Attackers aren’t limited to one platform, and your SOC can’t defend what it can’t see. One lightweight ZeroLock agent protects most major hypervisors, deploys in minutes, and streams every event into the SIEM and SOAR tools you already run, all while preserving performance, uptime, and control.
Lightweight
Rapid Deployment
Most Major Hypervisors
*Nutanix does not currently support third-party products running on AHV.
Flexible Deployment Options
Built into Your SOC
Broadcom-Signed VIB
Case Studies
ZeroLock in Action
See how organizations across sectors use ZeroLock to protect their core.

TECH SPECS
ZeroLock® Endpoint Agent Requirements for Hypervisors
OS
- VMware Cloud Foundation 9.X
- VMware ESXi, 6.7+ (Older versions supported upon request.)
- Nutanix-managed ESXi, 6.7+
- Nutanix AHV 2017+*
- XenServer, 6.5+
- Citrix Hypervisor, 8.0+
- XCP-ng 8.3+
- Proxmox, 3.0+
- Red Hat Enterprise Virtualization, 3.6+
- HPE Morpheus, 8.0+
- Dell VxRail, 4.8+
- KVM, Kernel 3.5+
* Note, Nutanix does not currently support third-party products running on AHV.
Processor
Memory
50MB
Disk Space
100MB
Kernel Mods.
No kernel modification or modules required
Installation Methods
- One-line, web-based deployment (Wget)
- File-based deployment (Tar.gz or Bash)
- VCF & ESXi: Signed VIB and deployable via vCenter
RAM
16GB
Disk Space
128GB (dependent on number of endpoints and data retention duration)
CPU Cores
6 or more recommended
Installation Reqs.
- Self-deployment: Latest version of Docker installed
- OVA-deployment: ESXi 7.0 or later
Documentation
Existing integrations
- SIEM: Splunk, Sumo Logic, Elastic, Google SecOps, CrowdStrike Next-Gen
- SOAR: Swimlane
- Incident API: Veeam
Cover Your Core Before the Next Attack
Modern attacks target the foundation of enterprise computing. ZeroLock stops them, catches what can get past, and undoes the damage before it becomes an incident.
Integrated with