Cover your core: Defense-in-Depth for Hypervisors & vCenter
Stop attacks before they start, catch what can get past, and undo the damage.
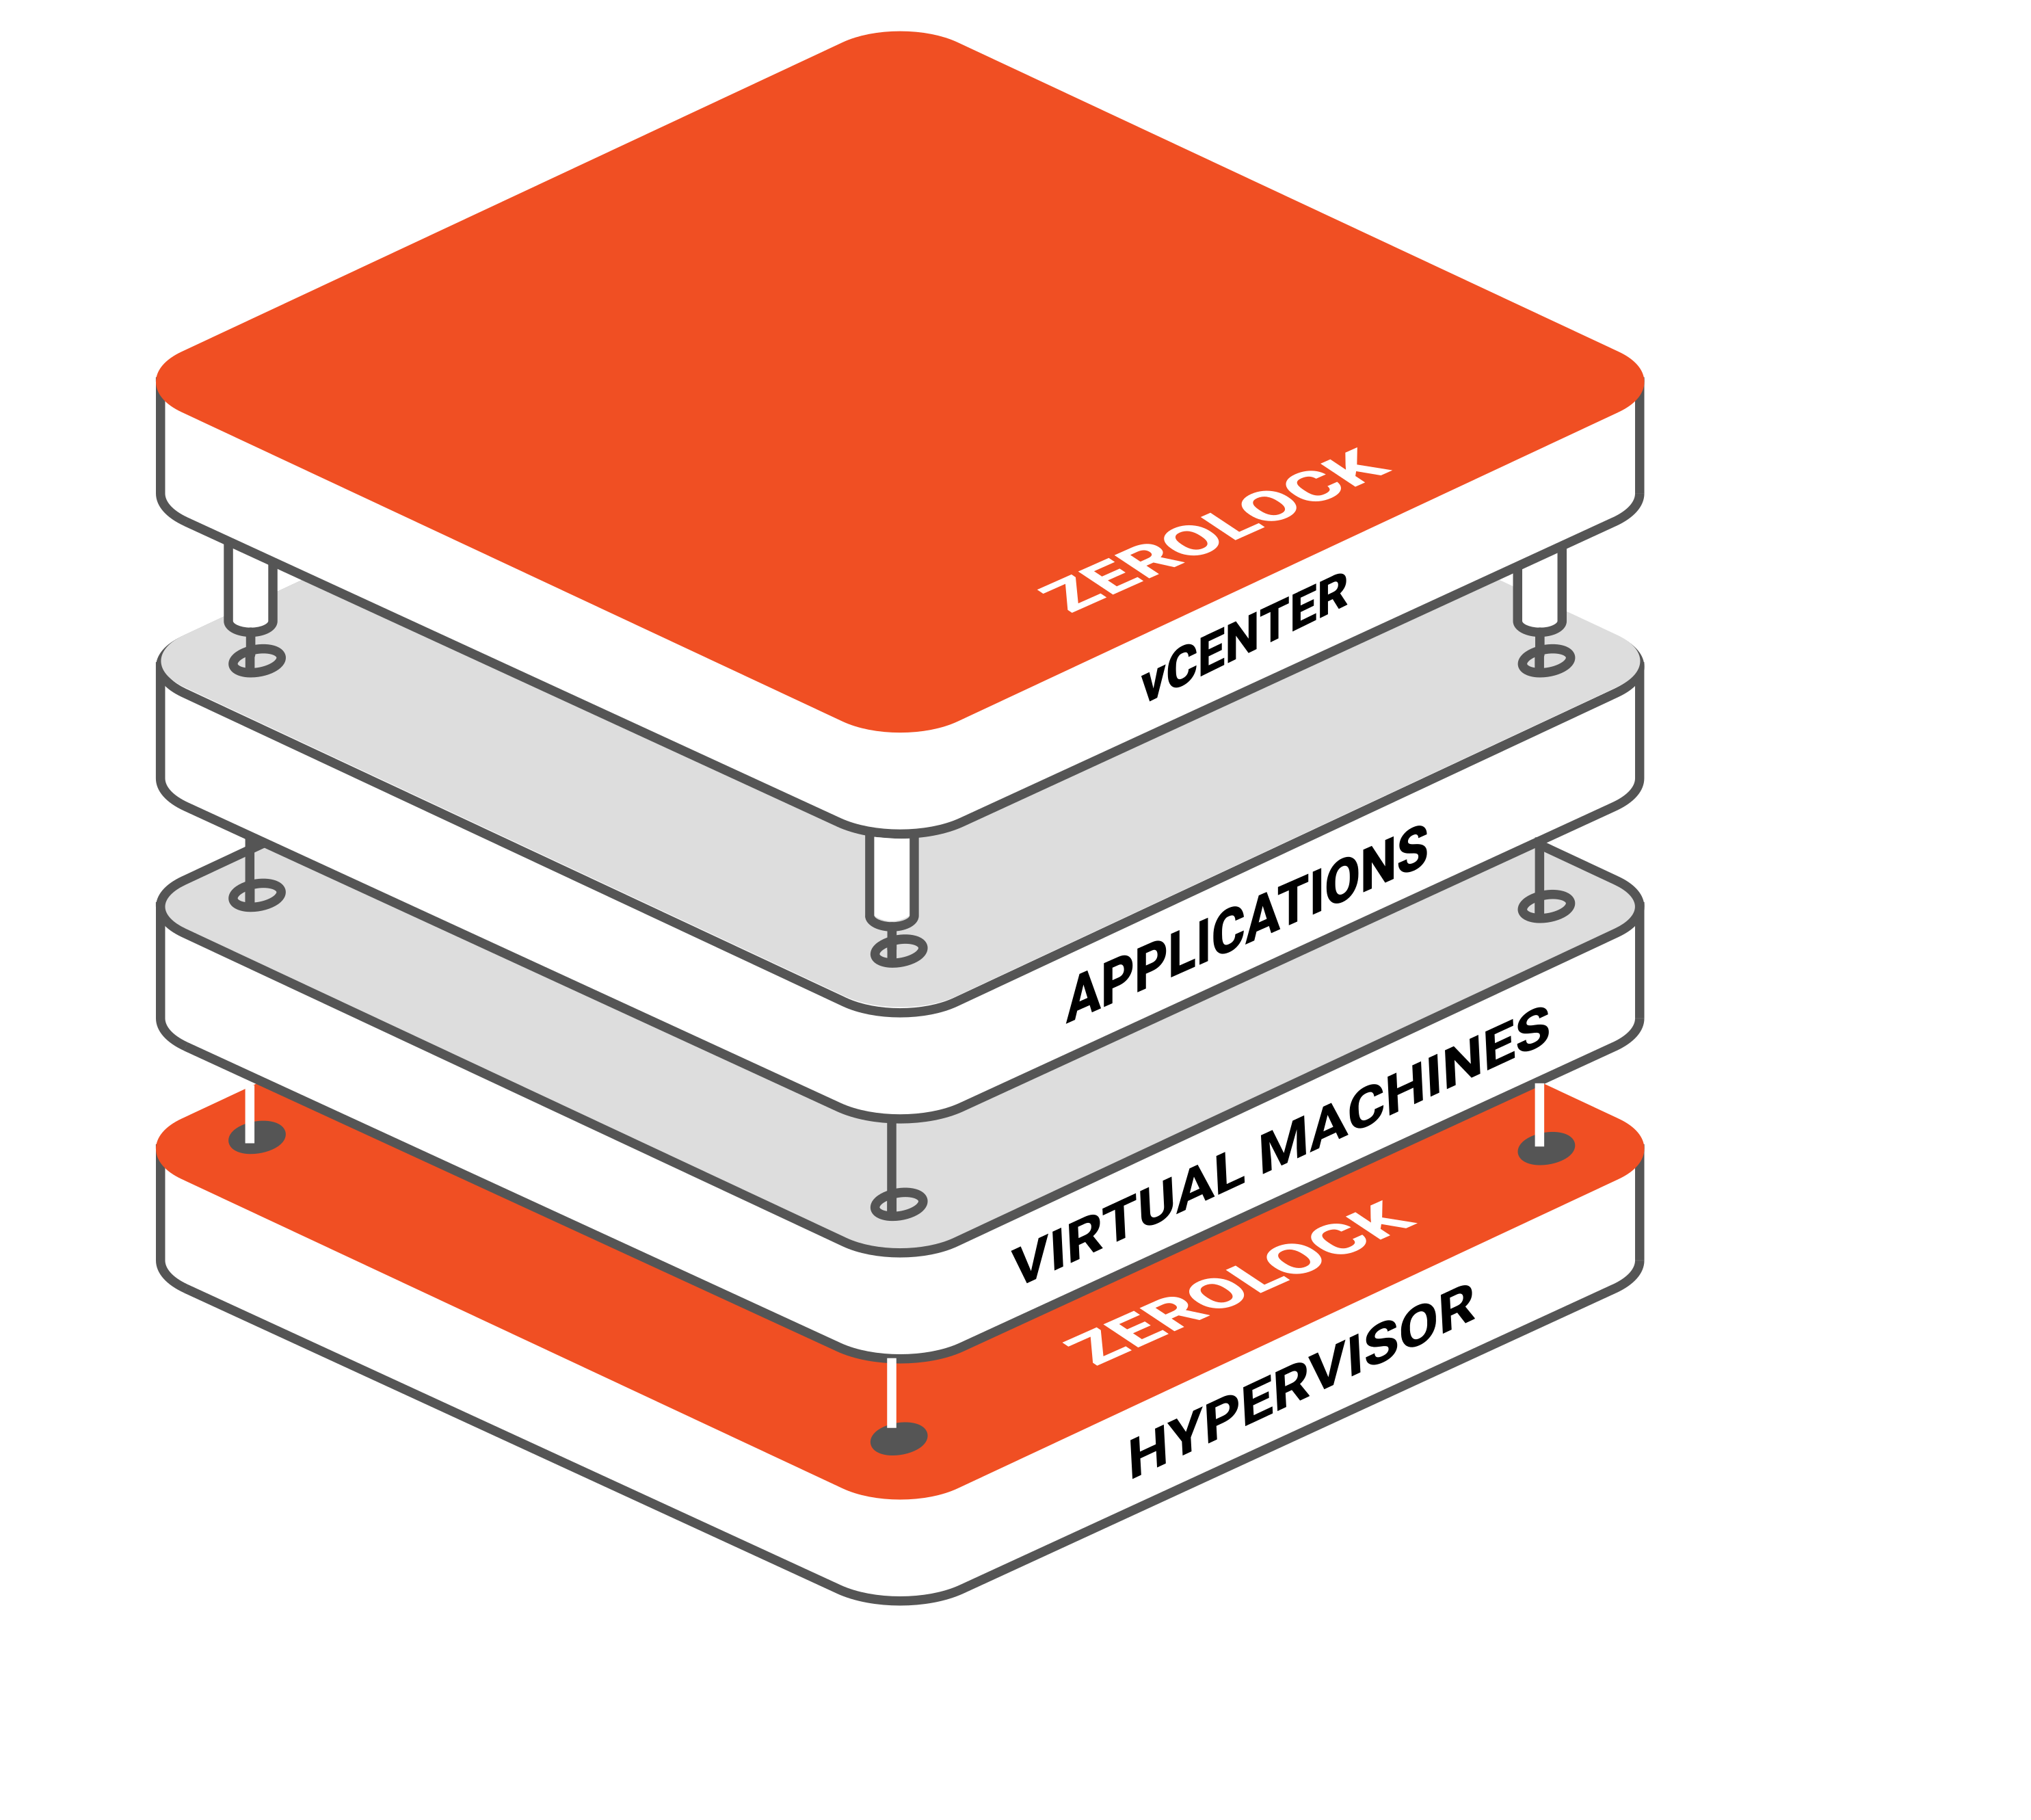
Compromise one hypervisor and every workload on it goes dark. ZeroLock® is a Broadcom-certified solution that provides defense-in-depth protection for the hypervisor. It’s also able to secure the management plane that controls it, where attacks cause the most damage.
Latest Threat Intelligence

Attackers are Targeting the Layer Your Security Stack Misses
growth in hypervisors’ share of ransomware encryption in 2025
for AI to turn a new CVE into a working exploit, for about $1
login credentials exposed in infostealer datasets in 2025
TTPs in the MITRE ATT&CK framework for ESX
When attackers control the hypervisor, they control every workload running on it.
ZeroLock stops attacks at the hypervisor, catches what can get past, and undoes the damage.
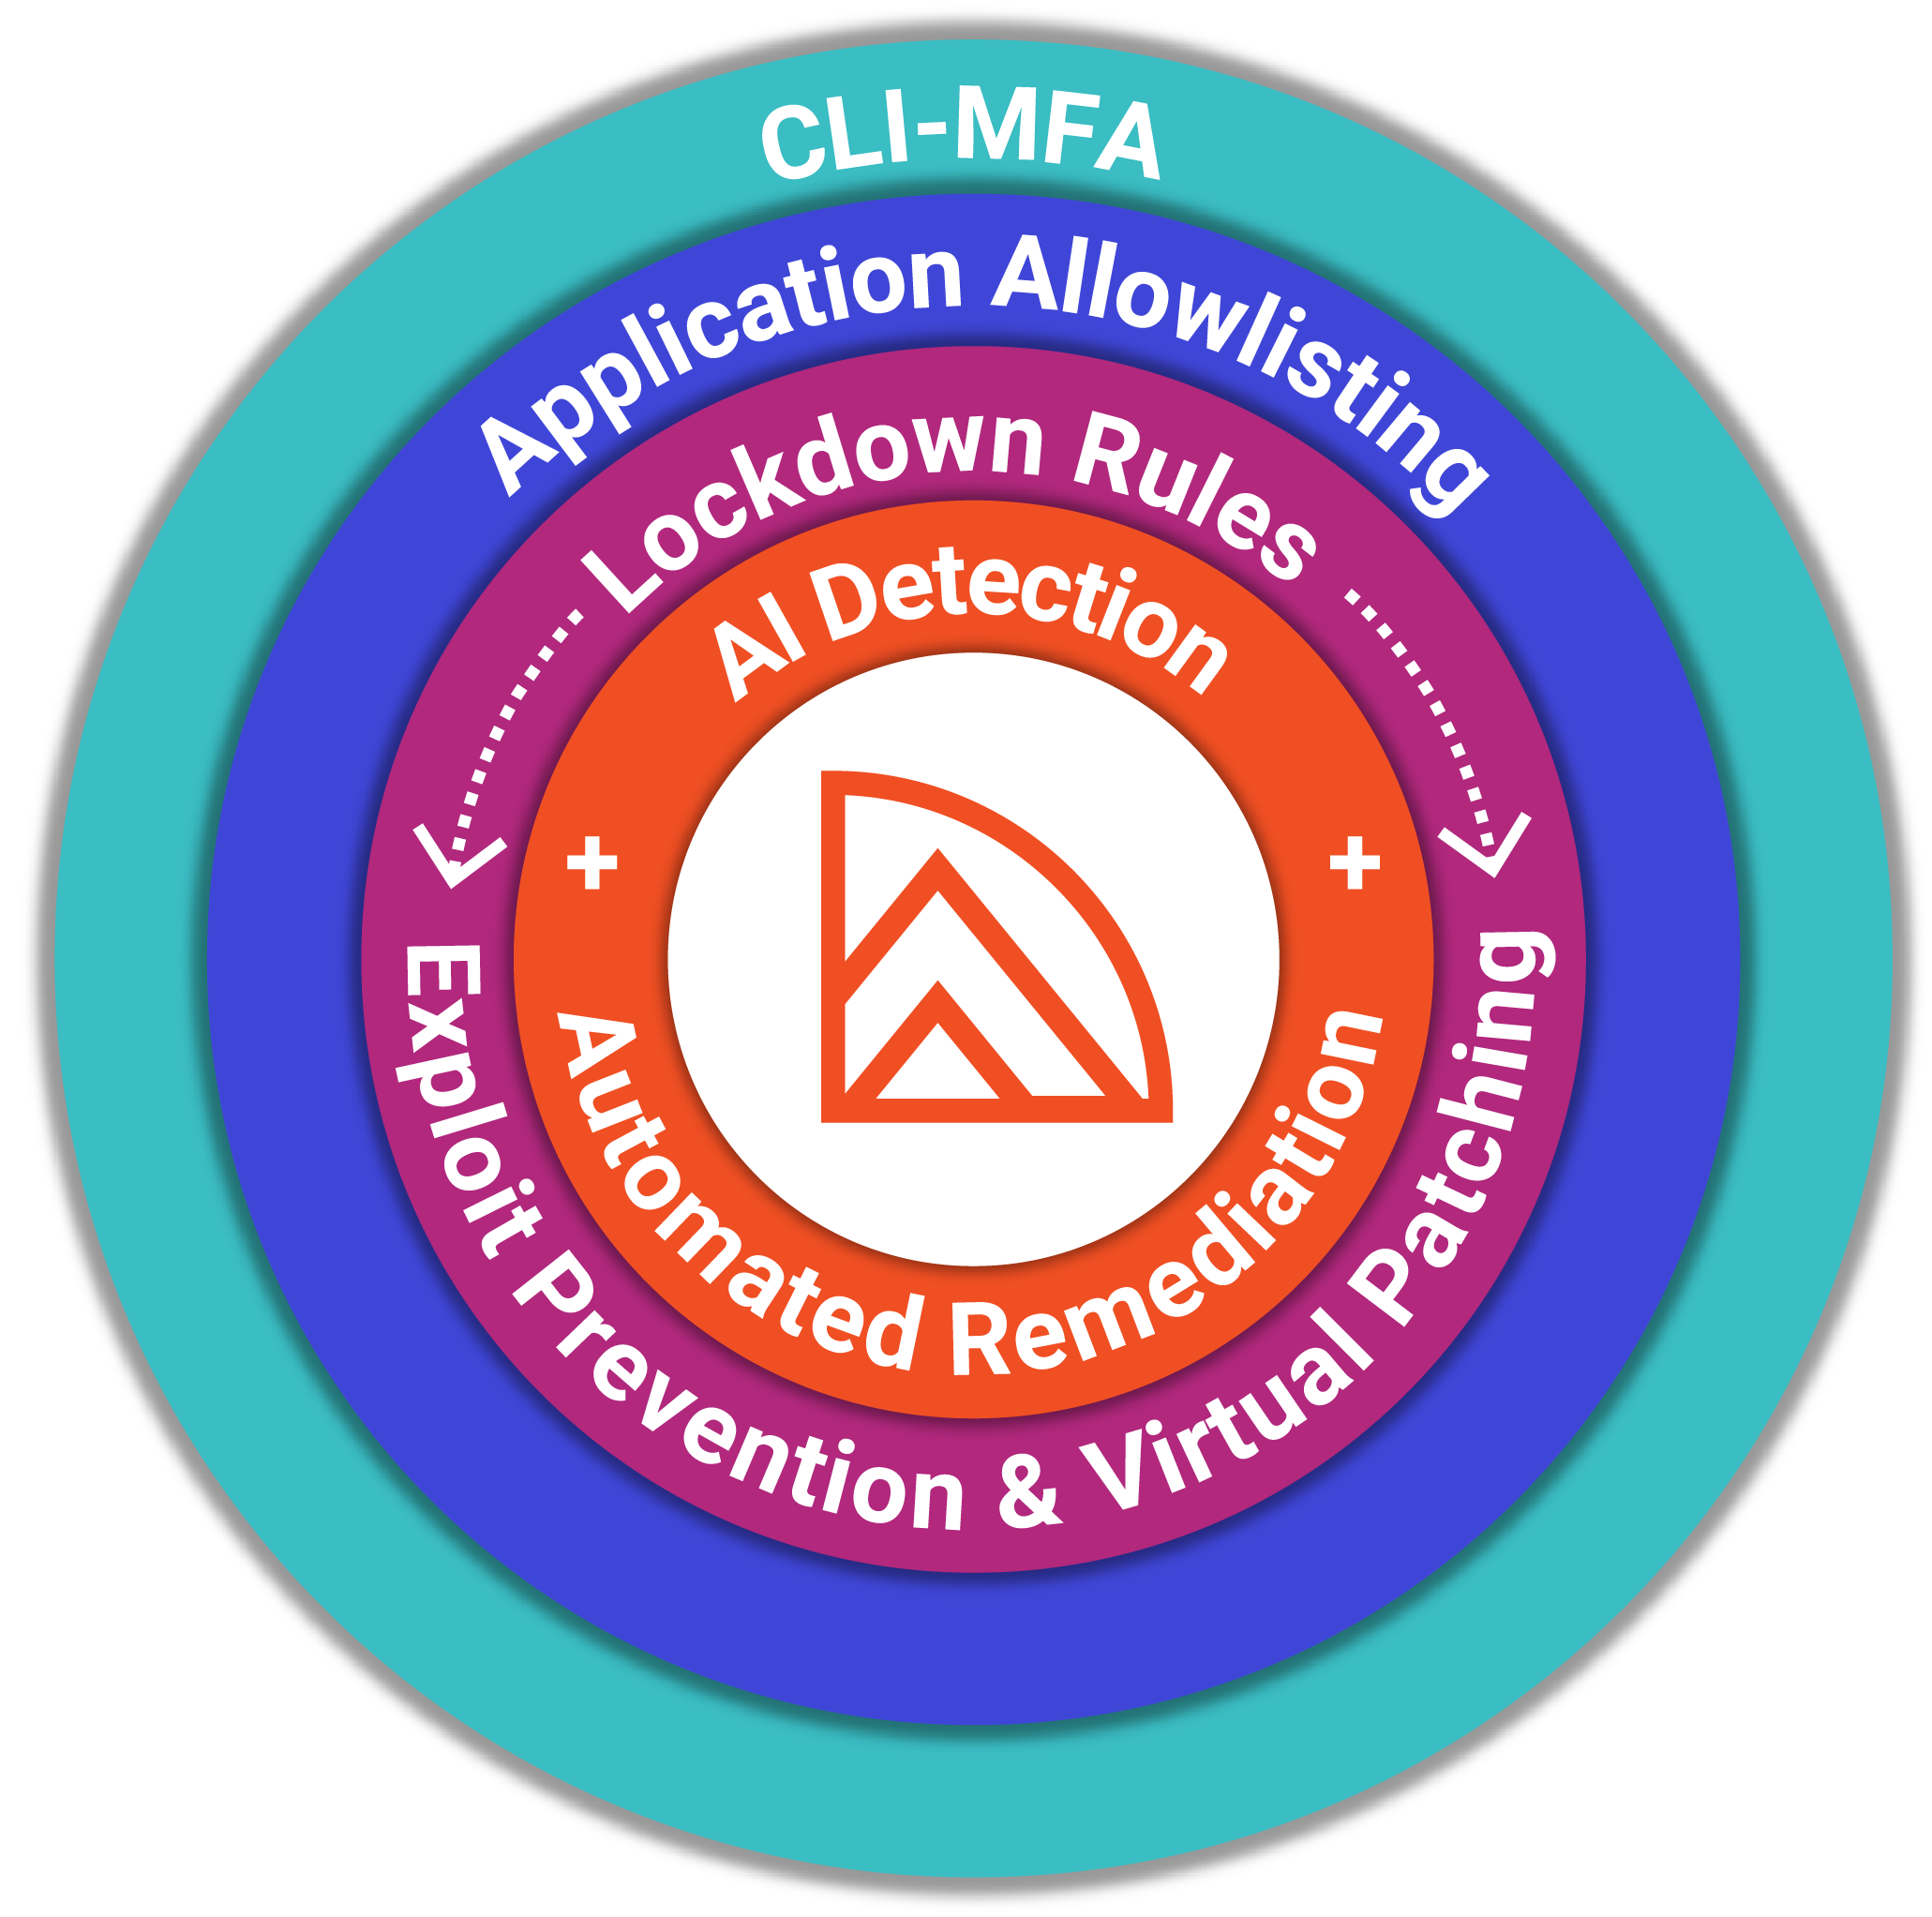
ZeroLock®: Defense-in-Depth for Hypervisors
Prevention is the first layer, not the last. Attackers log in with valid credentials and use the host’s own tools, where no rule fires and no SOC is looking. Certified by Broadcom, ZeroLock brings defense-in-depth to the hypervisor itself: it stops attacks, catches what can get past, and undoes the damage.
Preempt. Protect. Perform.
PREEMPT
Stop attacks before they start.
Most attacks begin with stolen credentials or misused admin tools. ZeroLock requires MFA on the commands you choose at the moment of action, not just at login.
Key Features
- CLI-MFA
- Exploit prevention & virtual patching
- Application allowlisting
- + more
PROTECT
Detect and undo what may get through.
No security strategy is static, which is why resilience matters as much as prevention. ZeroLock catches what can get past and rolls it back in seconds.
Key Features
- AI behavioral detection
- Ransomware & wiperware protection
- Automated file rollback
- + more
PERFORM
Built for how your team works.
One lightweight agent protects most major hypervisors, deploys in minutes, and streams every event into the SIEM and SOAR tools you already run.
Key Features
- Under 5% of one CPU core
- SaaS or air-gapped deployment
- Signed Broadcom VIB
- + more
Recognized by Industry Leaders
Recognized as a Key Startup in Security Software*
*Gartner, Emerging Tech: Techscape for Startups in Security Software.
Mitigates 100% of MITRE ATT&CK ESX techniques when properly configured and fully deployed
VMware Technology Alliance Partner with a signed Broadcom VIB
Protect the control room, too.
vCenter holds the keys to every host, every VM, and every credential. ZeroLock® brings the same defense-in-depth to the management plane..
Cover Your Core Before the Next Attack
Modern attacks target the foundation of enterprise computing. ZeroLock stops them, catches what can get past, and undoes the damage before it becomes an incident.
Integrated with